Read the incident and its alerts
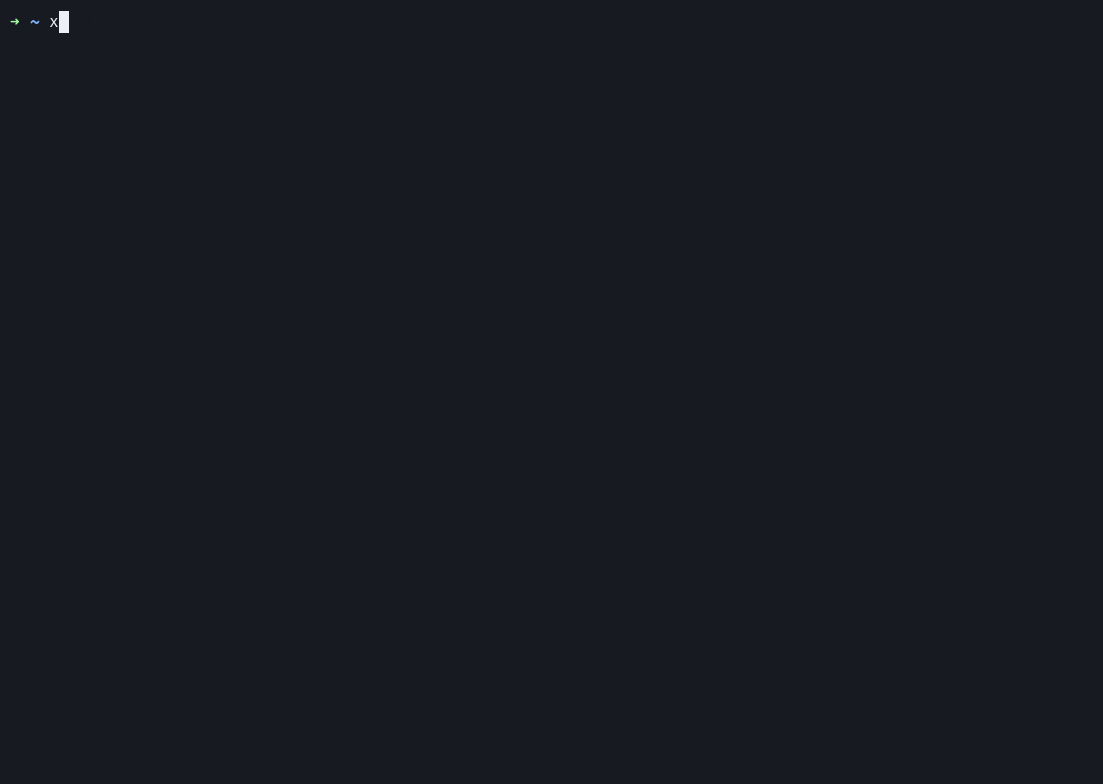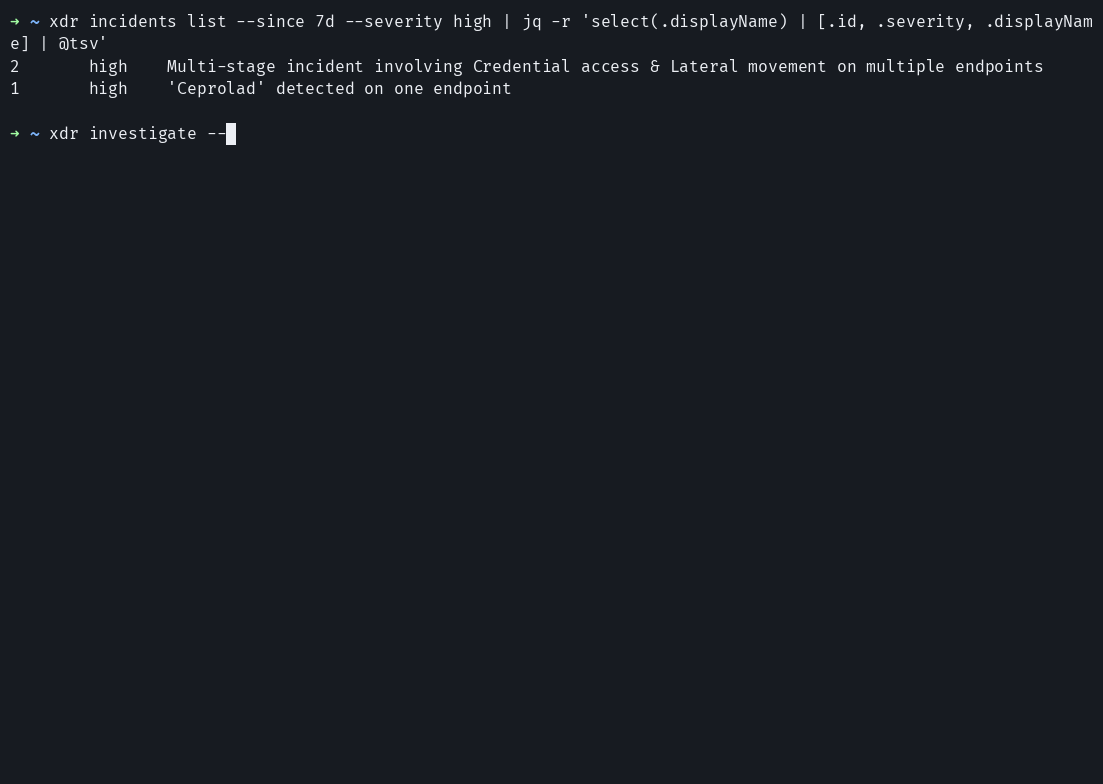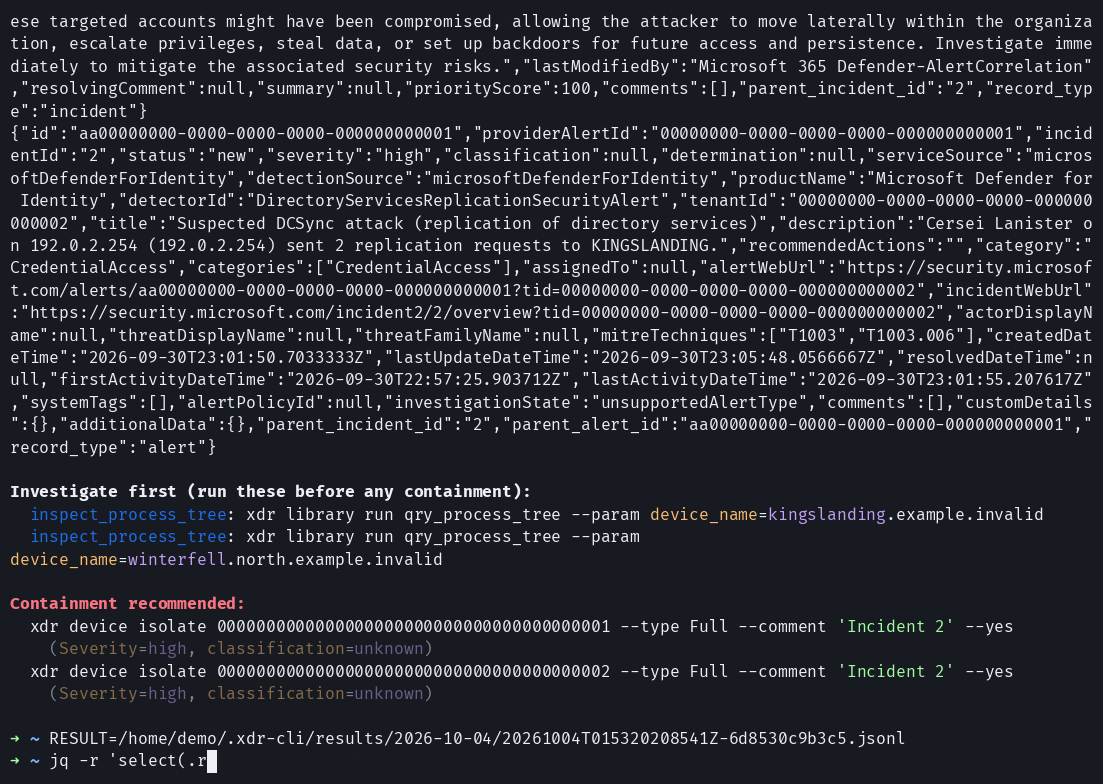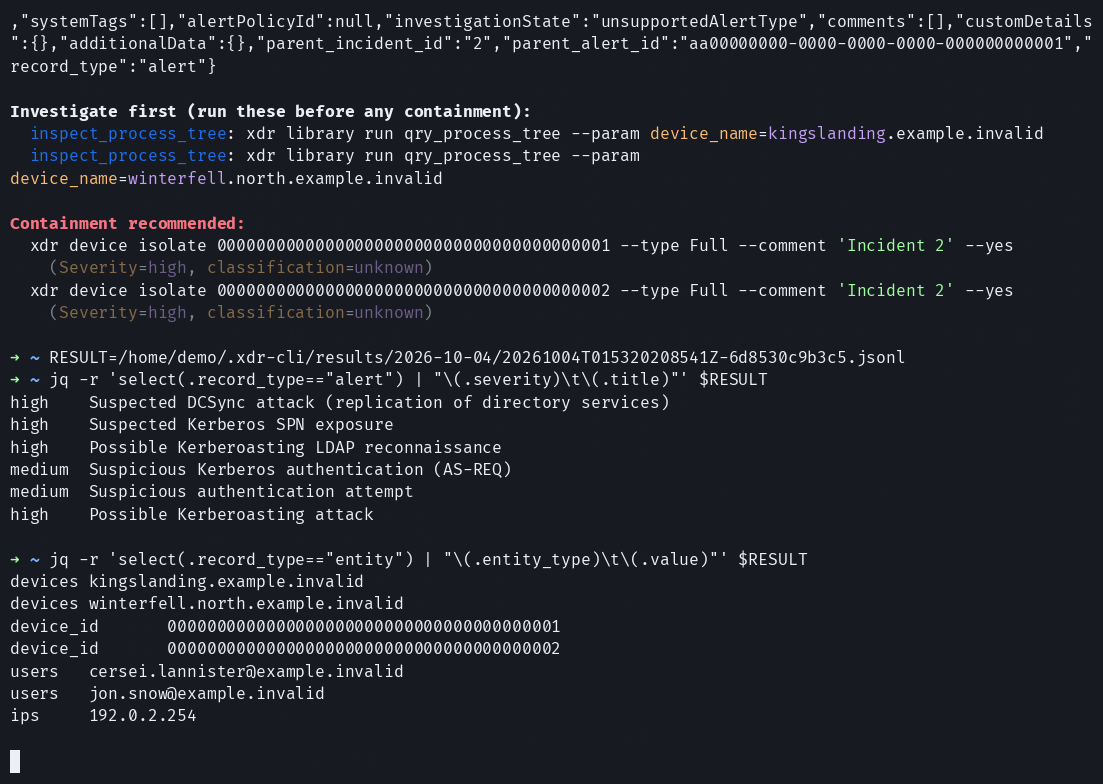
View alert evidence, including affected accounts and devices. The guided investigation extracts those entities and suggests queries to investigate them further.
Read the investigation guidexdr-cli is built for an AI agent to drive. Give your coding agent access to Defender incidents and advanced hunting, with investigation playbooks and output designed for its context window.
Put the coding-agent subscription you already have to work on incident triage.
pipx install "git+https://github.com/NerfBlasters/m365-xdr-cli.git"$ xdr incidents list --since 7d \
--severity high$ xdr incidents show 42 --expand alerts$ xdr investigate 42Read AGENTS.md, then investigate incident 42. Summarize the evidence and flag anything that needs my review.
Use an incident ID from your tenant.Point your agent at AGENTS.md and ask it to investigate an incident. The instructions cover how to gather evidence, choose hunts, and report what it found. You review its conclusions and decide on response actions.
xdr-cli saves large results locally and returns a compact receipt. An agent can inspect the evidence a few rows at a time, using the same xdr commands you can run yourself.
Start with the incident's alerts and evidence. Run a library query or your own KQL when you need more detail.
View alert evidence, including affected accounts and devices. The guided investigation extracts those entities and suggests queries to investigate them further.
Read the investigation guideThe query library covers common investigations and accepts parameters for the accounts, devices, or time range you're working with. You can also run KQL directly.
Browse the query libraryLarge results are saved as local JSONL files. A receipt tells you where to find them, so you can inspect the data with jq, grep, Python, or xdr results.
xdr investigate <incident-id>Watch a guided investigation from the terminal.
Use a portal session to try xdr-cli quickly, or set up an Entra app to use Microsoft's supported APIs.
Read the fu....n.. manual
Install xdr-cli and connect it to your Defender tenant.
02Find a hunting query and check which parameters it needs.
03Look up an alert title for investigation steps and common false positives.
04Set up an agent to use xdr-cli and read its results.